CVE-2026-14647: one loop, two lengths
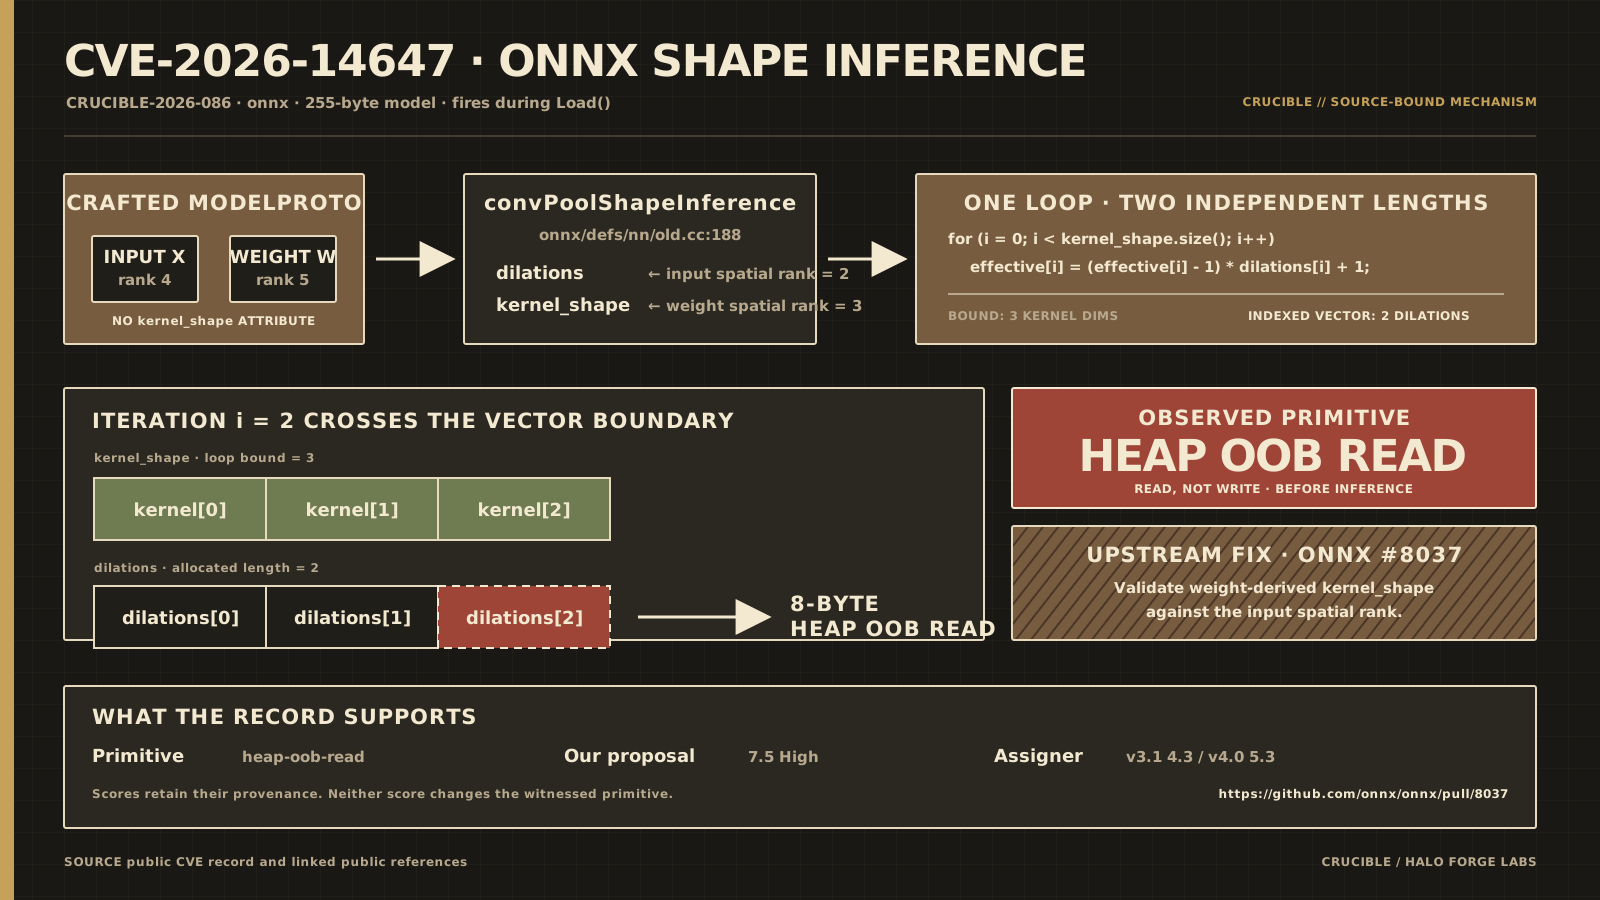
The crafted 255-byte ModelProto makes the input tensor rank 4 and the weight tensor rank 5, with no explicit kernel_shape. convPoolShapeInference therefore creates a two-element dilations vector from the input's spatial rank but derives a three-element kernel_shape from the weight. The loop is bounded by the latter and indexes the former: iteration 2 reads dilations[2] beyond the allocation.
What the evidence supports
- The fault is an 8-byte heap out-of-bounds read during
Load(), before inference. - It is not an out-of-bounds write and the diagram does not imply code execution.
- ONNX PR #8037 fixes the invariant by validating the weight-derived kernel shape against the input spatial rank.
- Our proposed score was 7.5 High; the assigner recorded CVSS v3.1 4.3 / v4.0 5.3. Both remain visible because provenance matters more than forcing agreement.
The CVE identity, primitive, scores, and public reference are read from the canonical ledger when this SVG is generated. Mechanism-specific facts come from the public CRUCIBLE-2026-086 advisory. Run go run ./tools/cveviz after either source changes; --check refuses stale output.
See the public CVE catalog for the complete disclosed set.