CVE-2026-17501: recursion without a limit
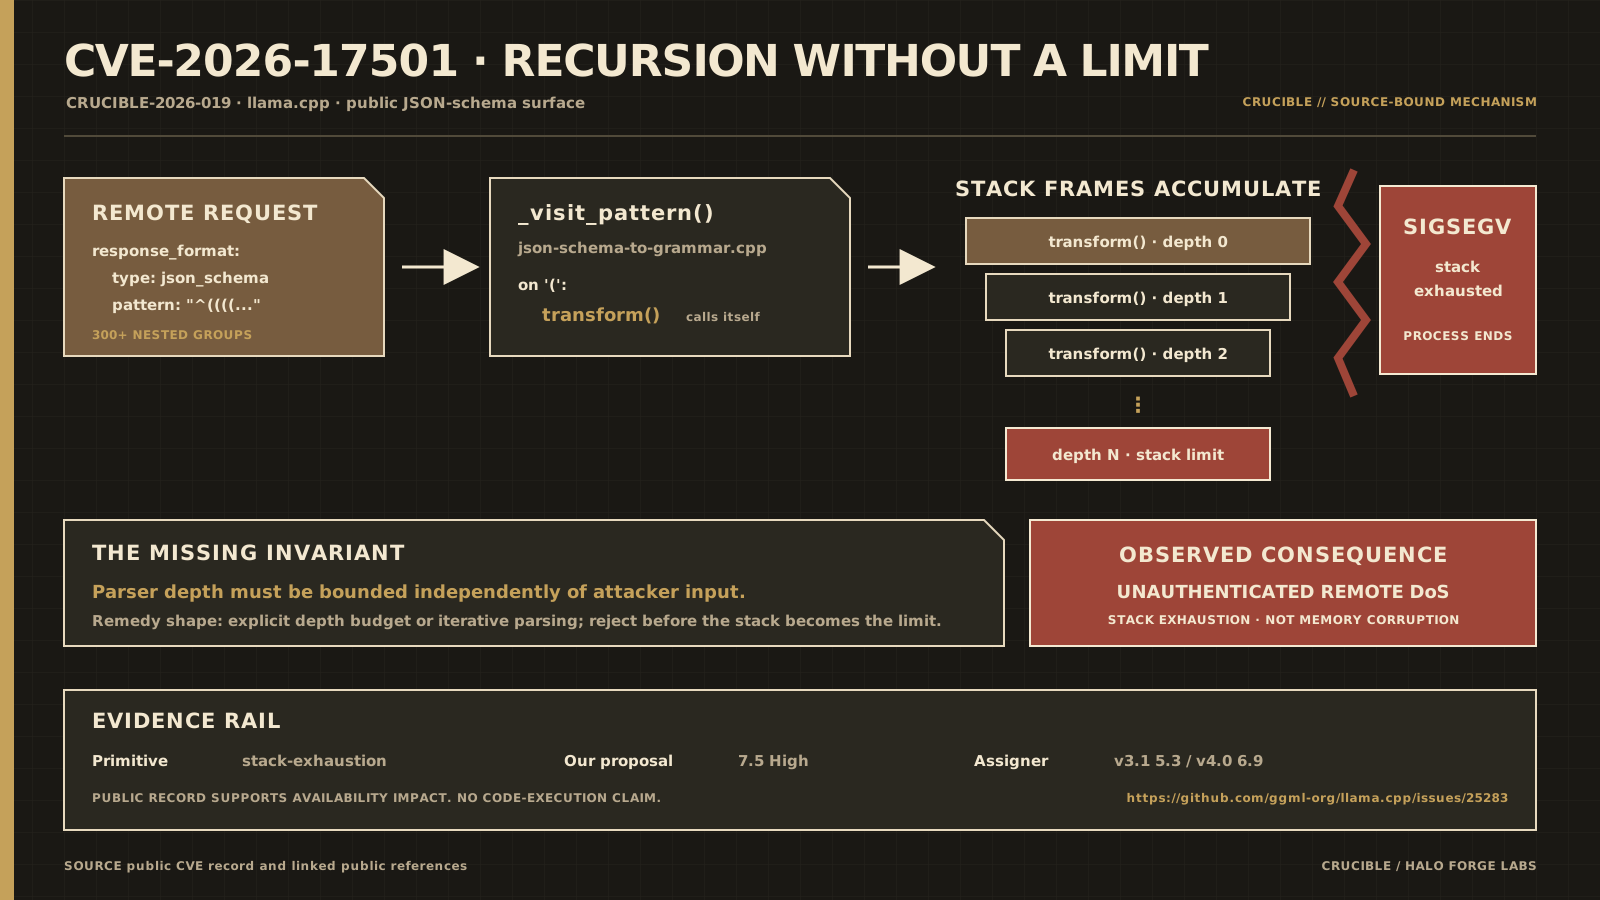
An unauthenticated request supplies a deeply nested regex pattern through the OpenAI-compatible JSON-schema response format. In _visit_pattern, every opening parenthesis makes the local transform() lambda call itself. Attacker input therefore controls call depth until the process stack, rather than an explicit parser budget, becomes the limit.
What the evidence supports
- The observed primitive is uncontrolled recursion leading to stack exhaustion and SIGSEGV.
- The demonstrated impact is remote process termination, not memory corruption or code execution.
- A durable remedy needs an explicit recursion budget or iterative parser; simply catching a later fault would not restore the invariant.
- Our proposed score was 7.5 High; the assigner recorded CVSS v3.1 5.3 / v4.0 6.9.
Sources: the canonical CVE ledger and the public CRUCIBLE-2026-019 advisory.